Zero Trust Architecture: The Ultimate Guide to Modern Enterprise Security

Learn how Zero Trust protects your organization against modern cyber threats and why Identity & Access Management plays a central role.

Traditional security models are increasingly reaching their limits in modern IT environments. Cloud platforms, hybrid work, mobile devices, and external access have long dissolved the traditional network perimeter. At the same time, the financial impact of successful cyberattacks continues to rise.
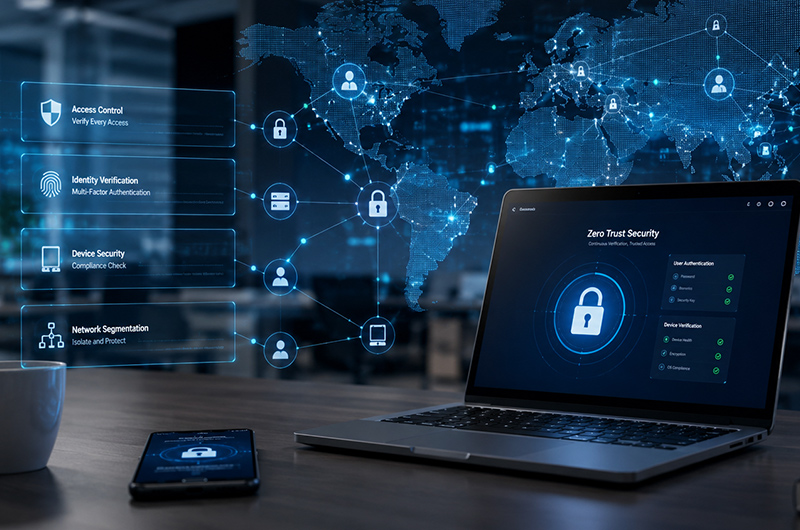
Zero Trust

According to IBM, the average global cost of a data breach reached USD 4.88 million in 2024, compared to USD 4.24 million in 2021. Organizations must therefore rethink security by focusing on identities, access, and data movement rather than network boundaries.

This is exactly where Zero Trust Security comes in: “Never trust, always verify.” No user, device, or system is trusted by default. Every access request is continuously verified and evaluated based on context. Particularly in hybrid IT environments with cloud services, remote work, and increasing identity-based attacks, Zero Trust is becoming the strategic foundation of modern cybersecurity.
Zero Trust am PC

Key Takeaways

Zero Trust Replaces the Traditional Security Perimeter

Modern IT environments can no longer be secured through network boundaries alone. Zero Trust Security continuously verifies every access request.

Identities Are at the Center of Modern Cybersecurity

User accounts, privileged access, and Non-Human Identities have become primary attack targets. As a result, Identity & Access Management (IAM) forms the foundation of every Zero Trust architecture.

Security Decisions Are Dynamic and Context-Aware

Zero Trust evaluates access requests in real time based on factors such as identity, device health, location, and user behavior. This enables organizations to detect risks early and automatically restrict access when necessary.

Zero Trust Strengthens Resilience and Supports Compliance

Through continuous verification, least-privilege principles, and transparent access controls, organizations reduce their attack surface, improve cyber resilience, and more effectively meet regulatory requirements such as GDPR, NIS2, and ISO 27001.

What Is Zero Trust?

Zero Trust is a modern security model based on the principle “Never trust, always verify.” Every request to access systems, applications, or data is continuously validated—regardless of whether the user is inside or outside the corporate network. Its objective is to minimize risk and consistently prevent unauthorized access.

Zero Trust Security: Why Traditional Security Models Are No Longer Enough

The traditional security concept of "trusted inside, untrusted outside" no longer works in today's IT environments. Cloud platforms, mobile work, and hybrid infrastructures have effectively eliminated the traditional network perimeter. At the same time, identity-based attacks and compromised user accounts continue to increase. As a result, Zero Trust has become a fundamental requirement for effective cybersecurity.

Organizations now operate within highly connected hybrid IT environments that include cloud services, external business partners, and distributed workforces. Applications and data are no longer hosted exclusively in on-premises data centers. Consequently, traditional security models based on clearly defined corporate network boundaries are rapidly losing their effectiveness.

Attackers exploit this increased complexity to move laterally through systems without being detected and to bypass existing security controls. Insider threats and compromised identities are particularly critical. Stolen credentials, abused privileged accounts, and legitimate user sessions often allow attackers to gain almost invisible access to sensitive systems.

Many security solutions detect these activities only at a late stage because they are performed using valid credentials and legitimate permissions. At the same time, the technical attack surface continues to grow. According to PwC, 75% of the 40,009 CVEs identified by NIST in 2024 required no user interaction whatsoever. As a result, security incidents are increasingly occurring automatically—without phishing clicks or human error.

This is exactly where Zero Trust Security comes into play: Trust is never assumed—it is continuously verified.

The Zero Trust Principle: Foundations and Core Elements

Zero Trust is based on the assumption that no user, device, or system should be inherently trusted, regardless of whether access originates from inside or outside the corporate network. Its objective is to continuously verify access requests, dynamically assess risk, and make security decisions based on contextual information.

1. Never Trust, Always Verify

The fundamental principle of Zero Trust is: “Never trust, always verify.” Every access request is treated as though it originates from a potentially untrusted network. Users, devices, and applications must therefore continuously prove their trustworthiness—regardless of whether they are operating within the corporate environment or accessing resources remotely.

Zero Trust consistently follows the principle of least privilege. Users and systems are granted only the access rights they need to perform their specific tasks—and only for as long as those permissions are required. This minimizes the potential impact of compromised accounts and prevents attackers from causing unnecessary damage.

In the Zero Trust model, security verification does not end after login. Authentication and access activities are continuously monitored and evaluated throughout the entire session. If a user’s behavior changes or the risk level increases, additional security measures can be triggered automatically.

Zero Trust does not evaluate access requests in isolation. Instead, it considers multiple contextual factors, enabling risks to be identified more accurately and security measures to be adjusted dynamically.

  • User Identity and Role
    Access requests are evaluated based on the user’s role, responsibilities, and permission level. For example, an administrator is granted different access rights than an external service provider.
  • Device Health and Compliance Status
    The system verifies whether the device complies with security policies—for example, by checking that security updates are current, encryption is enabled, and endpoint protection is active.
  • Location and Time
    Unusual login locations or access attempts outside normal business hours can increase the calculated risk and trigger additional verification steps.
  • Access Behavior (Anomaly-Based Analysis)
    Zero Trust continuously analyzes the behavior of identities. Unusual activities—such as abnormal data access patterns or sudden permission changes—are detected and evaluated automatically.

Zero Trust Architecture: How the Model Is Implemented Technically

Mann am PC

Zero Trust is not a single product but a security architecture composed of multiple interconnected components. Its goal is not to grant access by default but to continuously verify every request, dynamically assess risk, and make security decisions in real time.

To achieve this in practice, identities, networks, endpoints, and security analytics must work together seamlessly:

Identity & Access Management (IAM)

IAM is the core of a Zero Trust architecture. Authentication, Multi-Factor Authentication (MFA), role-based access control (RBAC), and access policies determine who is allowed to access which systems and data.

Network Segmentation

Microsegmentation divides networks into smaller security zones. Even if attackers gain access to a system, their ability to move laterally across the infrastructure is significantly restricted.

Authentication & Authorization

Access decisions are made dynamically and contextually in real time. Factors such as user role, device health, location, and risk score are continuously evaluated before access is granted.

Monitoring & Analytics

Zero Trust requires continuous monitoring of all access requests, activities, and behavioral patterns. Security solutions continuously analyze anomalies to detect suspicious activity at an early stage and respond automatically.

All of these components depend on a robust identity strategy—making Identity & Access Management (IAM) the foundation of Zero Trust.

Zero Trust Identity Management: Why IAM Is at the Center

Zero Trust places identity at the center of the security architecture. The corporate network is no longer considered the primary security perimeter. Instead, every individual identity—whether a user, device, or automated process—becomes the focal point of protection. As a result, Identity & Access Management (IAM) forms the foundation of every Zero Trust strategy.

According to SentinelOne, IAM solutions authenticate users and grant access only after verifying identity, context, and access risk. Trust is therefore no longer based on network location but exclusively on verified identity attributes.

In practice, Zero Trust builds upon existing IAM infrastructures and appropriate IAM tools. Directory services such as LDAP and Active Directory (AD), Single Sign-On (SSO), Multi-Factor Authentication (MFA), and role-based access models remain essential components of modern security architectures.

These technologies provide the technical foundation for centrally managing access, assigning granular permissions, and consistently enforcing security policies. Zero Trust extends these capabilities through continuous verification and dynamic real-time risk assessment.

Particular attention must be paid to non-human identities. Service accounts, APIs, automated processes, and machine-to-machine communications often possess extensive privileges while operating outside traditional user controls. At the same time, their number is growing rapidly in hybrid and cloud-based IT environments.

If these identities are not properly managed and continuously monitored, they become significant security risks. An effective Zero Trust Identity Management strategy must therefore provide visibility, protection, and continuous governance for all identities—human and non-human alike.

Implementing Zero Trust Step by Step

Implementing Zero Trust is not merely a technical deployment project but a strategic transformation initiative. Successful implementations do not follow a rigid blueprint. Instead, they are carried out in incremental phases, tailored to the existing IT landscape, organizational structure, and the organization's specific risk profile.

Step 1: Assess the Current IT Environment

The first step is to conduct a comprehensive assessment of the existing IT environment. This includes identifying all systems, applications, data flows, and identities—and understanding how they interact with one another. The objective is to gain a clear picture of the current architecture and all existing access paths.


Without this level of visibility, Zero Trust remains a theoretical concept. Organizations that lack insight into their identities and data flows cannot accurately assess risks or implement targeted security controls.

The second step is to systematically identify and classify all identities—including both human users and non-human identities such as service accounts, APIs, and automated processes. At the same time, all existing access rights and permission structures are analyzed.


This step is critical because IAM provides the foundation for all subsequent Zero Trust mechanisms. If identities and access models are documented incompletely or inconsistently, the result will be security gaps, excessive privileges, and a lack of transparency.

Based on the assessment, a tailored Zero Trust architecture is developed. There is no one-size-fits-all framework—every organization requires a model that aligns with its existing IT environment, applications, and business processes.


Zero Trust is explicitly not just a network security project. Focusing solely on network segmentation or perimeter security addresses only part of the challenge. Identities, applications, and data must all be considered equally to create a consistent security architecture.

Implementation should ideally follow an incremental approach. Rather than replacing the entire security architecture at once, organizations should begin with clearly defined pilot environments where Zero Trust principles can be tested and validated.


A “big bang” deployment carries significant risks, including technical complexity, operational disruption, and low user acceptance. A phased rollout enables controlled adjustments and continuous learning throughout the implementation process.

Zero Trust is not a one-time implementation project but an ongoing security strategy. New applications, evolving threats, and constantly changing IT environments require continuous updates to security policies and access models. 


Only through continuous monitoring, regular adjustments, and iterative improvements can a Zero Trust architecture remain effective and resilient against emerging cyber threats.

Benefits of Zero Trust Security – What Organizations Gain

Zero Trust Security delivers measurable business value by making security decisions based on identity, context, and risk. Instead of relying on implicit trust, it establishes a dynamic security model that continuously adapts to evolving IT environments and threat landscapes.

The Benefits:

  • Enhanced security through continuous verification of every access request
    Every access attempt is continuously verified—regardless of its source, network, or device—making unauthorized access significantly more difficult.
  • Greater visibility and control across the entire IT environment
    Organizations gain comprehensive visibility into identities, access permissions, and data flows across all systems.
  • Reduced attack risk, particularly from insider threats
    Because access is granted according to the Principle of Least Privilege and evaluated based on contextual risk, the likelihood of damage caused by compromised or misused accounts is significantly reduced.
  • Simplified compliance (GDPR, NIS2, ISO 27001)
    Centralized policies, comprehensive audit trails, transparent access decisions, and concepts such as Segregation of Duties (SoD) help organizations meet regulatory requirements more efficiently.
  • Scalability for complex and heterogeneous IT environments
    Zero Trust can be applied consistently across cloud, on-premises, and hybrid infrastructures, scaling alongside the organization’s IT landscape.
  •  

How OEDIV SecuSys Supports Your Zero Trust Journey

Implementing Zero Trust requires more than technical expertise—it demands a deep understanding of existing IT environments and identity infrastructures. OEDIV SecuSys supports organizations with vendor-independent consulting tailored to their individual requirements.

Rather than promoting specific products or vendors, the focus is on identifying the architecture, IAM framework, and security mechanisms that best fit each organization. This objective approach is particularly valuable in complex mid-sized and enterprise environments, where scalable and sustainable Zero Trust concepts are essential.

OEDIV SecuSys supports the entire journey—from strategy and design to implementation and ongoing operations. This end-to-end approach ensures that Zero Trust is not only defined as a strategy but also embedded effectively into daily operations. A particular focus is placed on Identity & Access Management (IAM) as the foundation of every Zero Trust architecture.

Organizations benefit from an integrated security strategy that consistently protects identities while maintaining secure and controlled access.

If you are looking to establish Zero Trust in a structured and sustainable way, OEDIV SecuSys is your trusted partner—from the initial assessment through continuous optimization of your security architecture.

Conclusion: Zero Trust Security – Identity as the New Security Perimeter

Zero Trust Security is no longer a theoretical security model—it is a necessary response to an IT landscape without a clearly defined network perimeter. Identities, access, and data flows have become the primary targets of modern cyberattacks.

Through continuous verification, context-aware decision-making, and ongoing validation, Zero Trust provides a security approach that reflects the realities of today's hybrid IT environments.

For organizations, Zero Trust Security delivers greater visibility, reduced attack surfaces, and significantly improved resilience against identity-based threats. Success, however, depends not only on the strategy itself but also on its effective implementation—particularly through a robust Identity & Access Management (IAM) framework serving as both the technical and organizational foundation.

Zero Trust Security has therefore become a core pillar of modern cybersecurity architectures. OEDIV SecuSys supports organizations with vendor-independent consulting, implementation, and managed services—all from a single source.


Zero Trust Security wird damit zum zentralen Baustein moderner Cybersecurity-Architekturen. Die OEDIV SecuSys unterstützt Sie dabei mit einer herstellerunabhängigen Beratung, Umsetzung und Betrieb aus einer Hand. Kontaktieren Sie uns für ein Erstgespräch.

FAQ

Zero Trust Security FAQ

Here you will find answers to the most important questions about our services and solutions.

What Is Zero Trust Security?

Zero Trust Security is a security model that does not automatically trust any access request. Every request is continuously verified—regardless of its origin, device, or network—and is granted only after its legitimacy has been confirmed, effectively preventing modern identity-based attacks.

The Zero Trust principle follows the motto “Never trust, always verify.” Every access request is consistently authenticated, authorized, and evaluated based on contextual risk—regardless of whether it originates from inside or outside the corporate network.

Identity & Access Management (IAM) is the foundation of Zero Trust. It manages identities, authenticates users, and controls access to resources. IAM enables granular permissions, Multi-Factor Authentication (MFA), and continuous governance for both human and non-human identities.

Zero Trust is implemented in phases through IT environment assessments, identity discovery, architecture design, pilot deployments, and continuous optimization. Existing IAM, network, and security solutions are integrated and enhanced throughout the process.

Zero Trust strengthens security through continuous verification, reduces attack surfaces, and minimizes insider risks. It also improves visibility, supports regulatory compliance, and scales effectively across complex hybrid IT environments.

Newsletter

Stay Informed

Subscribe to our newsletter to receive regular insights into Identity & Access Management.

    By subscribing, you agree to our Privacy Policy.

    Read More

    Related Articles

    Ready for an Initial Consultation?

    Let's assess together how resilient and future-ready your Identity & Access Management strategy really is.