CYBERSECURITY: Case Management and Automation with a Security Orchestration, Automation and Response (SOAR) Platform

A Security Operations Center (SOC) forms the foundation of an organization’s cybersecurity operations. By integrating a Security Orchestration, Automation and Response (SOAR) platform, the SOC can process security incidents more efficiently and respond significantly faster—an essential advantage, as speed is critical when mitigating cyber threats.

A SOAR platform combines compatible security technologies to collect and correlate security events from multiple sources. It can automatically process many incidents without requiring human intervention, helping organizations prioritize, standardize, and automate incident response while improving the overall efficiency of security operations.
CYBERSECURITY Case Management & SOAR

Threat and Vulnerability Management

Maintaining visibility into an organization’s overall security posture is one of the key responsibilities of the SOC, including the management of security vulnerabilities.

A SOAR platform supports the SOC by:

  • Prioritizing vulnerabilities based on risk
  • Streamlining remediation activities
  • Coordinating workflows across teams
  • Providing standardized reporting
  • Facilitating collaboration among all relevant stakeholders
These capabilities ensure that vulnerability management processes remain organized, transparent, and efficient.

Incident Response

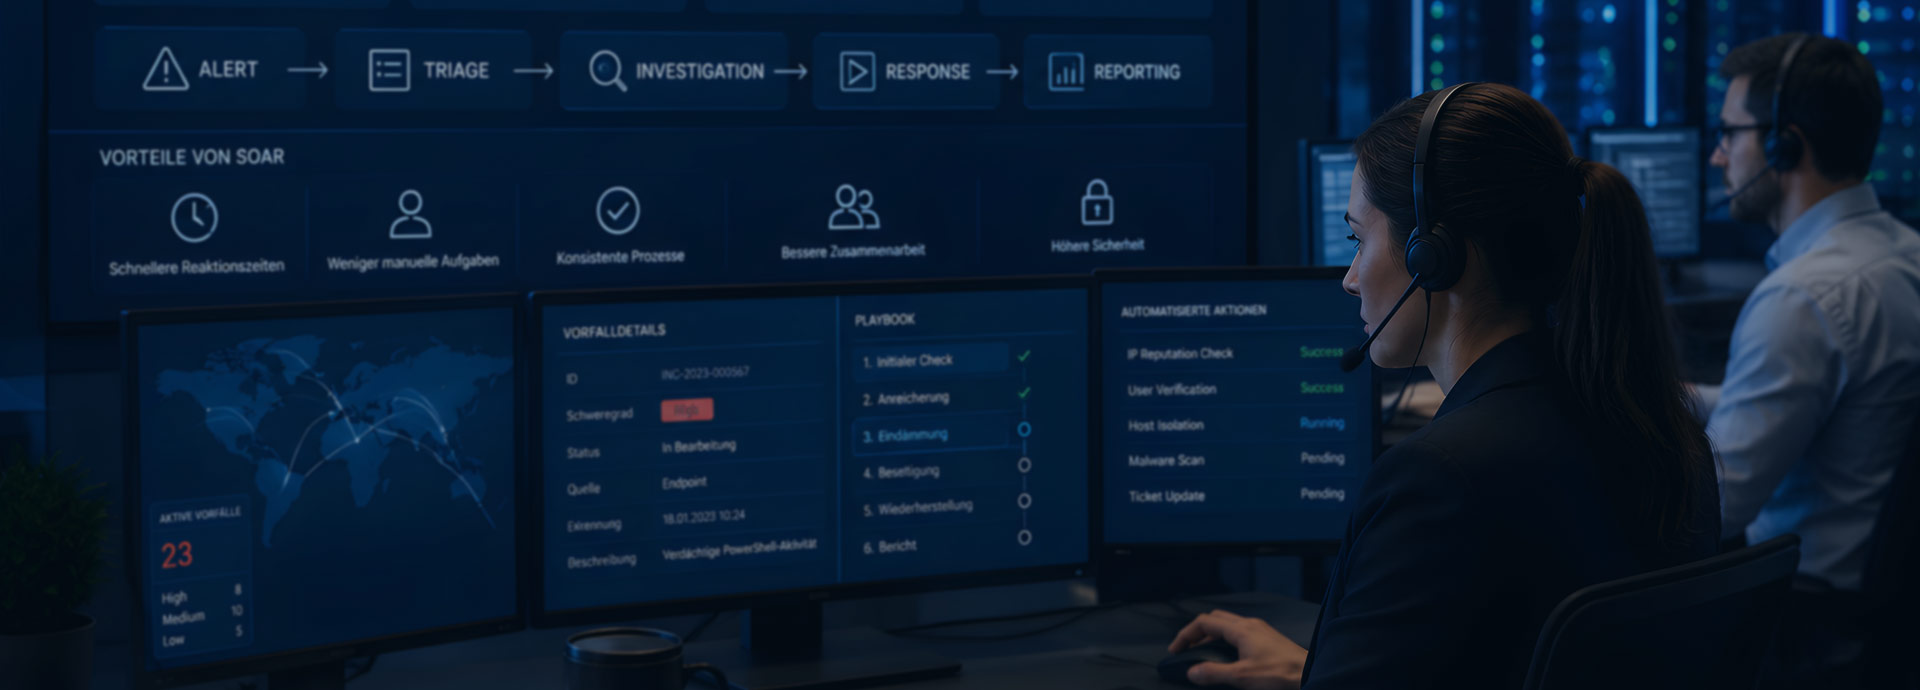
A SOAR solution provides security analysts with predefined workflows commonly known as playbooks that guide incident response activities. For example, when malware is detected, a playbook may define a structured decision tree:
  • If the malware is successfully removed, the incident can be closed.
  • If remediation fails, the affected device may be isolated in a quarantine network.
  • A full antivirus scan can then be initiated.
  • Additional response actions are performed until the incident has been fully resolved.

Security analysts may either follow these standardized procedures or adapt them when more complex situations require a different approach.

During large-scale security incidents, predefined processes are often insufficient. Thanks to bidirectional integrations with connected security solutions, a SOAR platform enables analysts to isolate compromised endpoints, contain threats, and prevent lateral movement across the network with only a few clicks.

Business stakeholders and technical departments can also be incorporated into automated workflows. For example, a playbook may request management approval before permanently disconnecting an infected device from the network and sending it for forensic investigation.

Automation and Security Operations

Once workflows have been defined, a SOAR platform can automate many response actions through its integrations with security technologies.

For example:
  • An endpoint reports malware detection.
  • The SOAR playbook automatically launches a full antivirus or EDR scan.
  • The affected endpoint is immediately isolated from the network.
  • Once the scan confirms the system is clean, network access is automatically restored.
  • If malware is still detected, a security analyst is notified for further investigation.

Many routine incidents can therefore be resolved automatically without manual intervention, allowing analysts to focus on more complex threats.

Centralized Case Management

Both SOAR and SIEM platforms aggregate data from connected security solutions.

If multiple security alerts relate to the same user account or endpoint, they can automatically be consolidated into a single case. This provides security teams with a complete overview of the incident while enriching the case with additional context, such as threat intelligence data and other relevant security information.

This centralized case management significantly improves investigation efficiency and accelerates incident response.

Newsletter

Stay Informed

Subscribe to our newsletter to receive regular insights into Identity & Access Management.

    By submitting this form, I consent to the processing of the data I have provided for the purpose of handling my enquiry.
    I may withdraw this consent at any time with future effect. Further information: Privacy Policy.
    Read More

    Related Articles

    Ready for an Initial Consultation?

    Let's assess together how resilient and future-ready your Identity & Access Management strategy really is.